

[Feb-2025] Use Real SC-200 Dumps Free Sample Questions and Practice Test Engine
Pass Microsoft SC-200 exam - questions - convert Tets Engine to PDF
NEW QUESTION # 84
You have an Azure subscription.
You need to delegate permissions to meet the following requirements:
Enable and disable Azure Defender.
Apply security recommendations to resource.
The solution must use the principle of least privilege.
Which Azure Security Center role should you use for each requirement? To answer, drag the appropriate roles to the correct requirements. Each role may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/security-center/security-center-permissions
NEW QUESTION # 85
You have a custom detection rule that includes the following KQL query.
For each of the following statements, select Yes if True. Otherwise select No.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation:
NEW QUESTION # 86
You have a Microsoft Sentinel workspace that contains an Azure AD data connector.
You need to associate a bookmark with an Azure AD-related incident.
What should you do? To answer, drag the appropriate blades to the correct tasks. Each blade may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content NOTE: Each correct selection is worth one point.
Answer:
Explanation:
NEW QUESTION # 87
You have a Microsoft Sentinel workspace named Workspace1 and 200 custom Advanced Security Information Model (ASIM) parsers based on the DNS schem a. You need to make the 200 parsers available in Workspace1. The solution must minimize administrative effort. What should you do first?
- A. Copy the parsers to the Azure Monitor Logs page.
- B. Create an XML file based on the DNS template.
- C. Create a YAML file based on the DNS template.
- D. Create a JSON file based on the DNS template.
Answer: A
NEW QUESTION # 88
You have a Microsoft 365 subscription that uses Microsoft Defender XDR.
You are investigating an attacker that is known to use the Microsoft Graph API as an attack vector. The attacker performs the tactics shown the following table.
You need to search for malicious activities in your organization.
Which tactics can you analyze by using the MicrosoftGraphActivityLogs table?
- A. Taclic1. Tac1ic2. andTactic3
- B. Tactic1 and Tactic2 only
- C. Tac1ic2 and Tactic3 only
- D. Tactic2 only
Answer: B
NEW QUESTION # 89
You have an Azure subscription that uses Microsoft Sentinel and contains 100 Linux virtual machines.
You need to monitor the virtual machines by using Microsoft Sentinel. The solution must meet the fallowing requirements:
* Minimize administrative effort
* Minimize the parsing required to read log data
What should you configure?
- A. a Log Analytics Data Collector API
- B. a Common Event Format (CEF) connector
- C. REST API integration
- D. a SysJog connector
Answer: D
NEW QUESTION # 90
You need to implement Azure Sentinel queries for Contoso and Fabrikam to meet the technical requirements.
What should you include in the solution? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/sentinel/extend-sentinel-across-workspaces-tenants
NEW QUESTION # 91
You have an Azure Functions app that generates thousands of alerts in Azure Security Center each day for normal activity.
You need to hide the alerts automatically in Security Center.
Which three actions should you perform in sequence in Security Center? Each correct answer presents part of the solution.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
1 - Select Security policy.
2 - Select Supperssion rules, and then select Create new suppression rule.
3 - Select Azure Resource as the entity type and specify the ID.
Reference:
https://techcommunity.microsoft.com/t5/azure-security-center/suppression-rules-for-azure-security-center-alerts-are-now/ba-p/1404920
NEW QUESTION # 92
You need to use an Azure Sentinel analytics rule to search for specific criteria in Amazon Web Services (AWS) logs and to generate incidents.
Which three actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.
a Microsoft 365 E5
Answer:
Explanation:
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/sentinel/detect-threats-custom
NEW QUESTION # 93
You need to create an advanced hunting query to investigate the executive team issue.
How should you complete the query? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
NEW QUESTION # 94
You have a Microsoft Sentinel workspace
You develop a custom Advanced Security information Model (ASIM) parser named Parser1 that produces a schema named Schema1.
You need to validate Schema1.
How should you complete the command? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation: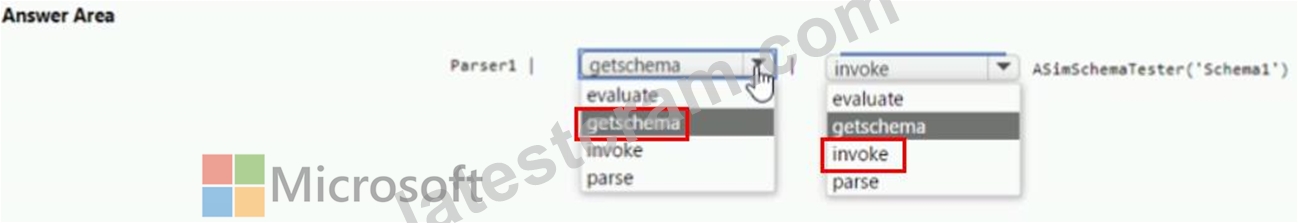
NEW QUESTION # 95
You use Azure Sentinel to monitor irregular Azure activity.
You create custom analytics rules to detect threats as shown in the following exhibit.
You do NOT define any incident settings as part of the rule definition.
Use the drop-down menus to select the answer choice that completes each statement based on the information presented in the graphic.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/sentinel/tutorial-detect-threats-custom
NEW QUESTION # 96
You need to implement Azure Defender to meet the Azure Defender requirements and the business requirements.
What should you include in the solution? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
NEW QUESTION # 97
You need to add notes to the events to meet the Azure Sentinel requirements.
Which three actions should you perform in sequence? To answer, move the appropriate actions from the list of action to the answer area and arrange them in the correct order.
Answer:
Explanation: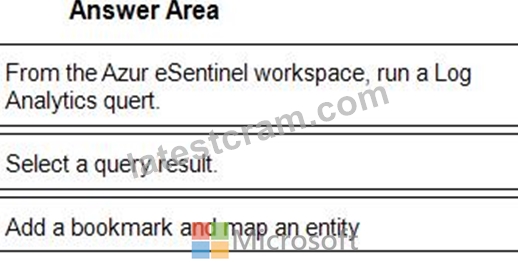
1 - From the Azur eSentinel workspace, run a Log Analytics quert.
2 - Select a query result.
3 - Add a bookmark and map an entity
Reference:
https://docs.microsoft.com/en-us/azure/sentinel/bookmarks
NEW QUESTION # 98
You need to create the test rule to meet the Azure Sentinel requirements.
What should you do when you create the rule?
- A. From Analytics rule details, configure the tactics.
- B. From Set rule logic, map the entities.
- C. From Set rule logic, turn off suppression.
- D. From Analytics rule details, configure the severity.
Answer: B
Explanation:
Section: [none]
Explanation/Reference:
https://docs.microsoft.com/en-us/azure/sentinel/tutorial-detect-threats-custom
NEW QUESTION # 99
You need to configure the Microsoft Sentinel integration to meet the Microsoft Sentinel requirements. What should you do? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation
NEW QUESTION # 100
You have a Microsoft Sentinel workspace that uses the Microsoft 365 Defender data connector.
From Microsoft Sentinel, you investigate a Microsoft 365 incident.
You need to update the incident to include an alert generated by Microsoft Defender for Cloud Apps.
What should you use?
- A. the Alerts page in the Microsoft 365 Defender portal
- B. the investigation graph on the Incidents page of Microsoft Sentinel
- C. the entity side panel of the Timeline card in Microsoft Sentinel
- D. the Timeline tab on the Incidents page of Microsoft Sentinel
Answer: C
NEW QUESTION # 101
DRAG DROP
You open the Cloud App Security portal as shown in the following exhibit.
Your environment does NOT have Microsoft Defender for Endpoint enabled.
You need to remediate the risk for the Launchpad app.
Which four actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.
Select and Place:
Answer:
Explanation:
Section: [none]
Explanation/Reference:
https://docs.microsoft.com/en-us/cloud-app-security/governance-discovery
NEW QUESTION # 102
You have a Microsoft Sentinel workspace.
You need to create a KQL query that will identify successful sign-ins from multiple countries during the last three hours.
How should you complete the query? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point
Answer:
Explanation:
NEW QUESTION # 103
You need to use an Azure Resource Manager template to create a workflow automation that will trigger an automatic remediation when specific security alerts are received by Azure Security Center.
How should you complete the portion of the template that will provision the required Azure resources? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/security-center/quickstart-automation-alert
NEW QUESTION # 104
You have a Microsoft 365 E5 subscription.
You plan to perform cross-domain investigations by using Microsoft 365 Defender.
You need to create an advanced hunting query to identify devices affected by a malicious email attachment.
How should you complete the query? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Reference:
https://docs.microsoft.com/en-us/microsoft-365/security/mtp/advanced-hunting-query-emails-devices?view=o365-worldwide
NEW QUESTION # 105
Your on-premises network contains 100 servers that run Windows Server.
You have an Azure subscription that uses Microsoft Sentinel.
You need to upload custom logs from the on-premises servers to Microsoft Sentinel.
What should you do? To answer, select the appropriate options m the answer area.
Answer:
Explanation:
NEW QUESTION # 106
......
Pass Your SC-200 Exam Easily - Real SC-200 Practice Dump Updated Feb 26, 2025: https://www.latestcram.com/SC-200-exam-cram-questions.html
2025 Realistic Verified Free Microsoft SC-200 Exam Questions: https://drive.google.com/open?id=1MU3Ps6AMViEvwpQ4RNoDvlfTCLmm3n-x
