

[2025] FCSS_EFW_AD-7.4 Dumps are Available for Instant Access
Valid FCSS_EFW_AD-7.4 Dumps for Helping Passing FCSS_EFW_AD-7.4 Exam!
NEW QUESTION # 28
Refer to the exhibit, which contains the output of a diagnose command.
Which two statements about the output are true? (Choose two.)
- A. This is an expected session created by a session helper
- B. Traffic in the original direction (coming from the IP address 10.171.121.38) will be routed to the next- hop IP address 10.200.1.1.
- C. This is an expected session created by an application control profile.
- D. Traffic in the original direction (coming from the IP address 10.171.121.38) will be routed to the next- hop IP address 10.0.1.10.
Answer: A,B
NEW QUESTION # 29
An administrator is configuring application control with FortiGate running in next-generation firewall (NGFW) policy-based mode.
Which two actions must the administrator take? (Choose two.)
- A. Configure the action as quarantine, if an application requires feedback to prevent instability.
- B. Specify an SSLISSH inspection profile on a consolidated policy.
- C. Configure central source network address translation (SNAT), if NAT is required.
- D. Create an application control profile and apply the profile to a firewall policy.
Answer: B,C
NEW QUESTION # 30
Refer to the exhibit, which shows an ADVPN network
An administrator must configure an ADVPN using IBGP and EBGP to connect overlay network 1 with 2.
What two options must the administrator configure in BGP? (Choose two.)
- A. set ebgp-enforce-multrhop enable
- B. set next-hop-self enable
- C. set ibgp-enforce-multihop advpn
- D. set attribute-unchanged next-hop
Answer: A,B
Explanation:
In thisADVPN (Auto-Discovery VPN) network, there are two hubs (Hub A and Hub B) connected via EBGP, whileIBGPis used within each overlay. To ensure proper BGP routing between the overlays, the administrator must configure specific BGP options..
set ebgp-enforce-multihop enable
By default, EBGP requires directly connected neighbors. Since Hub A and Hub B are not directly connected but reach each other over an IPsec tunnel, multihop must be enabled for EBGP sessions to work.
set next-hop-self enable
In IBGP, the next-hop attribute does not change by default. When an IBGP route is advertised from a spoke to another hub or spoke, the next-hop needs to be updated to ensure proper reachability. Enabling next-hop-self forces the BGP speaker to advertise itself as the next-hop, ensuring that all spokes properly reach routes across the overlays.
NEW QUESTION # 31
A company's guest internet policy, operating in proxy mode, blocks access to Artificial Intelligence Technology sites using FortiGuard. However, a guest user accessed a page in this category using port 8443.
Which configuration changes are required for FortiGate to analyze HTTPS traffic on nonstandard ports like 8443 when full SSL inspection is active in the guest policy?
- A. Add a URL wildcard domain to the website CA certificate and use it in the SSL/SSH Inspection Profile.
- B. To analyze nonstandard ports in web filter profiles, use TLSv1.3 in the SSL/SSH Inspection Profile.
- C. In the Protocol Port Mapping section of the SSL/SSH Inspection Profile, enter 443, 8443 to analyze both standard (443) and non-standard (8443) HTTPS ports.
- D. Administrators can block traffic on nonstandard ports by enabling the SNI check in the SSL/SSH Inspection Profile.
Answer: C
Explanation:
When FortiGate is operating in proxy mode with full SSL inspection enabled, it inspects encrypted HTTPS traffic by default on port 443. However, some websites may use non-standard HTTPS ports (such as 8443), which FortiGate does not inspect unless explicitly configured.
To ensure that FortiGate inspects HTTPS traffic on port 8443, administrators must manually add port 8443 in the Protocol Port Mapping section of the SSL/SSH Inspection Profile. This allows FortiGate to treat HTTPS traffic on port 8443 the same as traffic on port 443, enabling proper inspection and enforcement of FortiGuard category-based web filtering.
NEW QUESTION # 32
Refer to the exhibit, which contains the partial output of a diagnose command.

Based on the output, which two statements are correct? (Choose two.)
- A. DPD is disabled.
- B. Anti-replay is enabled.
- C. The remote gateway IP is 10.200.5.1.
- D. The remote gateway has quick mode selectors containing a destination subnet of 10.1.2.0/24.
Answer: B,D
NEW QUESTION # 33
An administrator must improve the resiliency of a link by minimizing data loss within the enterprise network that has full path redundancy.
What should the administrator enable on the FortiGate devices that use BGP as dynamic routing protocol between two separate autonomous systems? (Choose two.)
- A. graceful-restart
- B. route-reflector-client
- C. ibgp-multipath
- D. bfd
Answer: A,D
NEW QUESTION # 34
Refer to the exhibit, which shows a partial enterprise network.
An administrator would like the area 0.0.0.0 to detect the external network.
What must the administrator configure?
- A. Set the area 0.0.0.l type to stub on FortiGate A and B.
- B. Configure a virtual link between FortiGate A and B.
- C. Enable RIP redistribution on FortiGate B.
- D. Configure a distribute-route-map-in on FortiGate B.
Answer: C
Explanation:
The diagram shows a multi-area OSPF network where:
FortiGate A is in OSPF Area 0 (Backbone area).
FortiGate B is in OSPF Area 0.0.0.1 and is connected to an RIP network.
To ensure that OSPF Area 0 (0.0.0.0) learns routes from the external RIP network, FortiGate B must redistribute RIP routes into OSPF.
Steps to achieve this:
1. Enable route redistribution on FortiGate B to inject RIP-learned routes into OSPF.
2. This allows OSPF Area 0.0.0.1 to forward RIP routes to OSPF Area 0 (0.0.0.0), making the external network visible.
NEW QUESTION # 35
Why does the ISDB block layers 3 and 4 of the OSI model when applying content filtering? (Choose two.)
- A. FortiGate has a predefined list of all IPs and ports for specific applications downloaded from FortiGuard.
- B. The ISDB limits access by URL and domain.
- C. The ISDB works in proxy mode, allowing the analysis of packets in layers 3 and 4 of the OSI model.
- D. The ISDB blocks the IP addresses and ports of an application predefined by FortiGuard.
Answer: A,D
Explanation:
TheInternet Service Database (ISDB)in FortiGate is used to enforce content filtering atLayer 3 (Network Layer) and Layer 4 (Transport Layer)of the OSI model by identifying applications based on their predefined IP addresses and ports.
FortiGate has a predefined list of all IPs and ports for specific applications downloaded from FortiGuard:
# FortiGate retrieves and updates apredefined listof IPs and ports for different internet services from FortiGuard.
# This allows FortiGate to block specific services atLayer 3 and Layer 4without requiring deep packet inspection.
The ISDB blocks the IP addresses and ports of an application predefined by FortiGuard:
# ISDB works by matching traffic to knownIP addresses and portsof categorized services.
# When an application or service is blocked, FortiGate prevents communication bydenying traffic based on its destination IP and port number.
NEW QUESTION # 36
Refer to the exhibit.
An administrator is deploying a hub and spokes network and using OSPF as dynamic protocol.
Which configuration is mandatory for neighbor adjacency?
- A. Set bfd enable in the router configuration
- B. Set virtual-link enable in the hub interface
- C. Set network-type point-to-multipoint in the hub interface
- D. Set rfc1583-compatible enable in the router configuration
Answer: C
Explanation:
In a hub-and-spoke topology using OSPF over IPsec VPNs, thepoint-to-multipointnetwork type is necessary to establish neighbor adjacencies between the hub and spokes. This network type ensures that OSPF operates correctly without requiring a designated router (DR) and allows dynamic routing updates across the IPsec tunnels.
NEW QUESTION # 37
A company that acquired multiple branches across different countries needs to install new FortiGate devices on each of those branches. However, the IT staff lacks sufficient knowledge to implement the initial configuration on the FortiGate devices.
Which three approaches can the company take to successfully deploy advanced initial configurations on remote branches? (Choose three.)
- A. Use provisioning templates and install configuration settings at the device layer.
- B. Apply Jinja in the FortiManager scripts for large-scale and advanced deployments.
- C. Use metadata variables to dynamically assign values according to each FortiGate device.
- D. Use the Global ADOM to deploy global object configurations to each FortiGate device.
- E. Add FortiGate devices on FortiManager as model devices, and use ZTP or LTP to connect to FortiGate devices.
Answer: A,C,E
Explanation:
Use metadata variables to dynamically assign values according to each FortiGate device:
Metadata variables in FortiManager allow device-specific configurations to be dynamically assigned without manually configuring each FortiGate. This is especially useful when deploying multiple devices with similar base configurations.
Use provisioning templates and install configuration settings at the device layer:
Provisioning templates in FortiManager provide a structured way to configure FortiGate devices.
These templates can define interfaces, policies, and settings, ensuring that each device is correctly configured upon deployment.
Add FortiGate devices on FortiManager as model devices, and use ZTP or LTP to connect to FortiGate devices:
Zero-Touch Provisioning (ZTP) and Local Touch Provisioning (LTP) help automate the deployment of FortiGate devices. By adding devices as model devices in FortiManager, configurations can be pushed automatically when devices connect for the first time, reducing manual effort.
NEW QUESTION # 38
Which three tasks are part of the manual registration process for adding a FortiGate device to FortiManager for central management? (Choose three.)
- A. Wait for the rating databases to download on FortiManager.
- B. Add the FortiManager IP address to the FortiGate central management configuration.
- C. In FortiManager, add the unregistered FortiGate device.
- D. Start the rating services on FortiManager.
- E. Import the policy package from the managed FortiGate device.
Answer: B,C,E
NEW QUESTION # 39
A company's users on an IPsec VPN between FortiGate A and B have experienced intermittent issues since implementing VXLAN. The administrator suspects that packets exceeding the 1500- byte default MTU are causing the problems.
In which situation would adjusting the interface's maximum MTU value help resolve issues caused by protocols that add extra headers to IP packets?
- A. Adjust the MTU on interfaces only if FortiGate has the FortiGuard enterprise bundle, which allows MTU modification.
- B. Adjust the MTU on interfaces in all FortiGate devices that support the latest family of Fortinet SPUs: NP7, CP9 and SP5.
- C. Adjust the MTU on interfaces only in wired connections like PPPoE, optic fiber, and ethernet cable.
- D. Adjust the MTU on interfaces in controlled environments where all devices along the path allow MTU interface changes.
Answer: D
Explanation:
When using IPsec VPNs and VXLAN, additional headers are added to packets, which can exceed the default 1500-byte MTU. This can lead to fragmentation issues, dropped packets, or degraded performance.
To resolve this, the MTU (Maximum Transmission Unit) should be adjusted only if all devices in the network path support it. Otherwise, some devices may still drop or fragment packets, leading to continued issues.
Why adjusting MTU helps:
VXLAN adds a 50-byte overhead to packets.
IPsec adds additional encapsulation (ESP, GRE, etc.), increasing the packet size. If packets exceed the MTU, they may be fragmented or dropped, causing intermittent connectivity issues.
Lowering the MTU on interfaces ensures packets stay within the supported size limit across all network devices.
NEW QUESTION # 40
Which two statements about bulk configuration changes using FortiManager CLI scripts are correct?
(Choose two.)
- A. When executed on the Policy Package, ADOM database, changes are applied directly to the managed FortiGate.
- B. When executed on the Remote FortiGate directly, administrators do not have the option to review the changes prior to installation.
- C. When executed on the All FortiGate in ADOM, changes are automatically installed without creating a new revision history.
- D. When executed on the Device Database, you must use the installation wizard to apply the changes to the managed FortiGate
Answer: B,D
NEW QUESTION # 41
Refer to the exhibit, which shows a LAN interface connected from FortiGate to two FortiSwitch devices.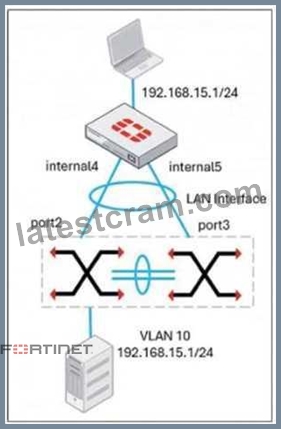
What two conclusions can you draw from the corresponding LAN interface? (Choose two.)
- A. This connection is using a FortiLInk to manage VLANs on FortiGate.
- B. The LAN interface must use a 802.3ad type interface.
- C. You must enable STP or RSTP on FortiGate and FortiSwitch to avoid layer 2 loopbacks.
- D. FortiGate is using an SD-WAN-type interface to connect to a FortiSwitch device with MCLAG.
Answer: A,B
Explanation:
The diagram shows a FortiGate connected to two FortiSwitches, which suggests the use of FortiLink, Fortinet's protocol for managing switches directly from a FortiGate. Since multiple connections are being used, the LAN interface must be set to 802.3ad (LAG) mode to aggregate the links for redundancy and load balancing.
This setup allows FortiGate to handle VLAN assignments dynamically, as seen with VLAN 10 (192.168.15.1/24). FortiLink ensures seamless integration between FortiGate and FortiSwitches, making STP unnecessary because Fortinet's MCLAG prevents loops at Layer 2. SD-WAN, on the other hand, is used for WAN interfaces and does not apply to switch connectivity in this scenario.
NEW QUESTION # 42
Refer to the exhibit, which shows a physical topology and a traffic log.
The administrator is checking on FortiAnalyzer traffic from the device with IP address10.1.10.1, located behind the FortiGate ISFW device.
The firewall policy in on the ISFW device does not have UTM enabled and the administrator is surprised to see a log with the actionMalware, as shown in the exhibit.
What are the two reasons FortiAnalyzer would display this log? (Choose two.)
- A. ISFW is in a Security Fabric environment.
- B. The firewall policy in NGFW-1 has UTM enabled.
- C. ISFW is not connected to FortiAnalyzer and must go through NGFW-1.
- D. Security rating is enabled in ISFW.
Answer: A,B
Explanation:
From the exhibit, ISFW is part of a Security Fabric environment with NGFW-1 as the Fabric Root. In this architecture, FortiGate devices share security intelligence, including logs and detected threats.
ISFW is in a Security Fabric environment:
# Security Fabric allows devices like ISFW toreceive threat intelligencefrom NGFW-1, even if UTM is not enabled locally.
# If NGFW-1 detects malware fromIP 10.1.10.1 to 89.238.73.97, this information can bepropagated to ISFW and FortiAnalyzer.
The firewall policy in NGFW-1 has UTM enabled:
# Even thoughISFW does not have UTM enabled, NGFW-1 (which sits between ISFW and the external network)does have UTM enabledand is scanning traffic.
# Since NGFW-1 detects malware in the session, it logs the event, which is then sent toFortiAnalyzer.
NEW QUESTION # 43
......
Updated FCSS_EFW_AD-7.4 Dumps Questions For Fortinet Exam: https://www.latestcram.com/FCSS_EFW_AD-7.4-exam-cram-questions.html
UPDATED Fortinet FCSS_EFW_AD-7.4 Exam Questions & Answer: https://drive.google.com/open?id=1U-6MrHPQfkNmyZngyBg7TCFSvvvrV-95
